TL;DR

Get business pricing on monitors, keyboards and dev gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Microsoft’s November 10, 2026, security release lists 1,094 Microsoft CVEs, following 1,474 in October. One Outlook flaw was exploited before its fix; Microsoft has not disclosed how many November vulnerabilities were found with AI. A separate Paint vulnerability has a reported fix, but some users may not yet have received the patched version.
Microsoft’s November 10, 2026, security release lists 1,094 Microsoft CVEs, including an Outlook flaw exploited before a fix was available. The release also renews questions about the pace of Microsoft’s vulnerability disclosures and arrives amid reports that a separate Paint fix may not yet have reached all users.
The figure comes from Microsoft’s Security Update Guide release notes. Krebs on Security counted 1,093 fixes published on November 10; the one-item difference is CVE-2026-109469, a Critical Entra Device Registration flaw published November 5. Microsoft says no customer action is needed for that issue. The November data file contains entries from other vendors as well, but the source analysis says those were excluded from the 1,094 Microsoft-CVE total.
The most urgent item identified in the source is CVE-2026-124194 in Outlook. Opening a crafted file can expose a user’s NTLMv2 password hash, according to the source material. The U.S. Cybersecurity and Infrastructure Security Agency added the vulnerability to its catalog of exploited flaws on November 10. The source recommends prioritizing Outlook and Office updates, followed by relevant Critical server fixes.
A separate issue affects Microsoft Paint. The source says CVE-2026-83844 was published October 13 and that the version Microsoft initially identified as fixed remained vulnerable, according to German publication heise. Microsoft named version 11.2609.401.0 as the working version on November 6. PC Gamer reported that the update was still not appearing for some users; checking the Microsoft Store is suggested in the source.
Prioritize Outlook and Paint Updates
The exploited Outlook vulnerability gives administrators a specific reason to act quickly: attacks were reported before the patch, and the described impact involves exposure of an authentication hash. The source does not say how widespread exploitation is, so the known fact is that the flaw was listed as exploited, not how many people or organizations were affected.
The overall CVE count also affects how security teams plan patching. The release notes list 726 Windows CVEs, alongside 174 for Office, 59 for SQL Server, 53 for Developer Tools and smaller totals across other product families. Those figures do not mean every flaw affects every installation. Administrators need to match affected products and severity to the systems they manage, while individual users should install applicable updates and separately check Paint.
Products Worth Considering

Bose QuietComfort True Wireless Earbuds with Active Noise Cancellation, Bluetooth 5.3, USB-C Charging, IPX4, Black

Apple Watch SE 3 GPS 40mm Smartwatch

Logitech MX Mechanical Wireless Illuminated Keyboard, Tactile Quiet, Graphite
As an affiliate, we earn on qualifying purchases.
A Rising Monthly CVE Count
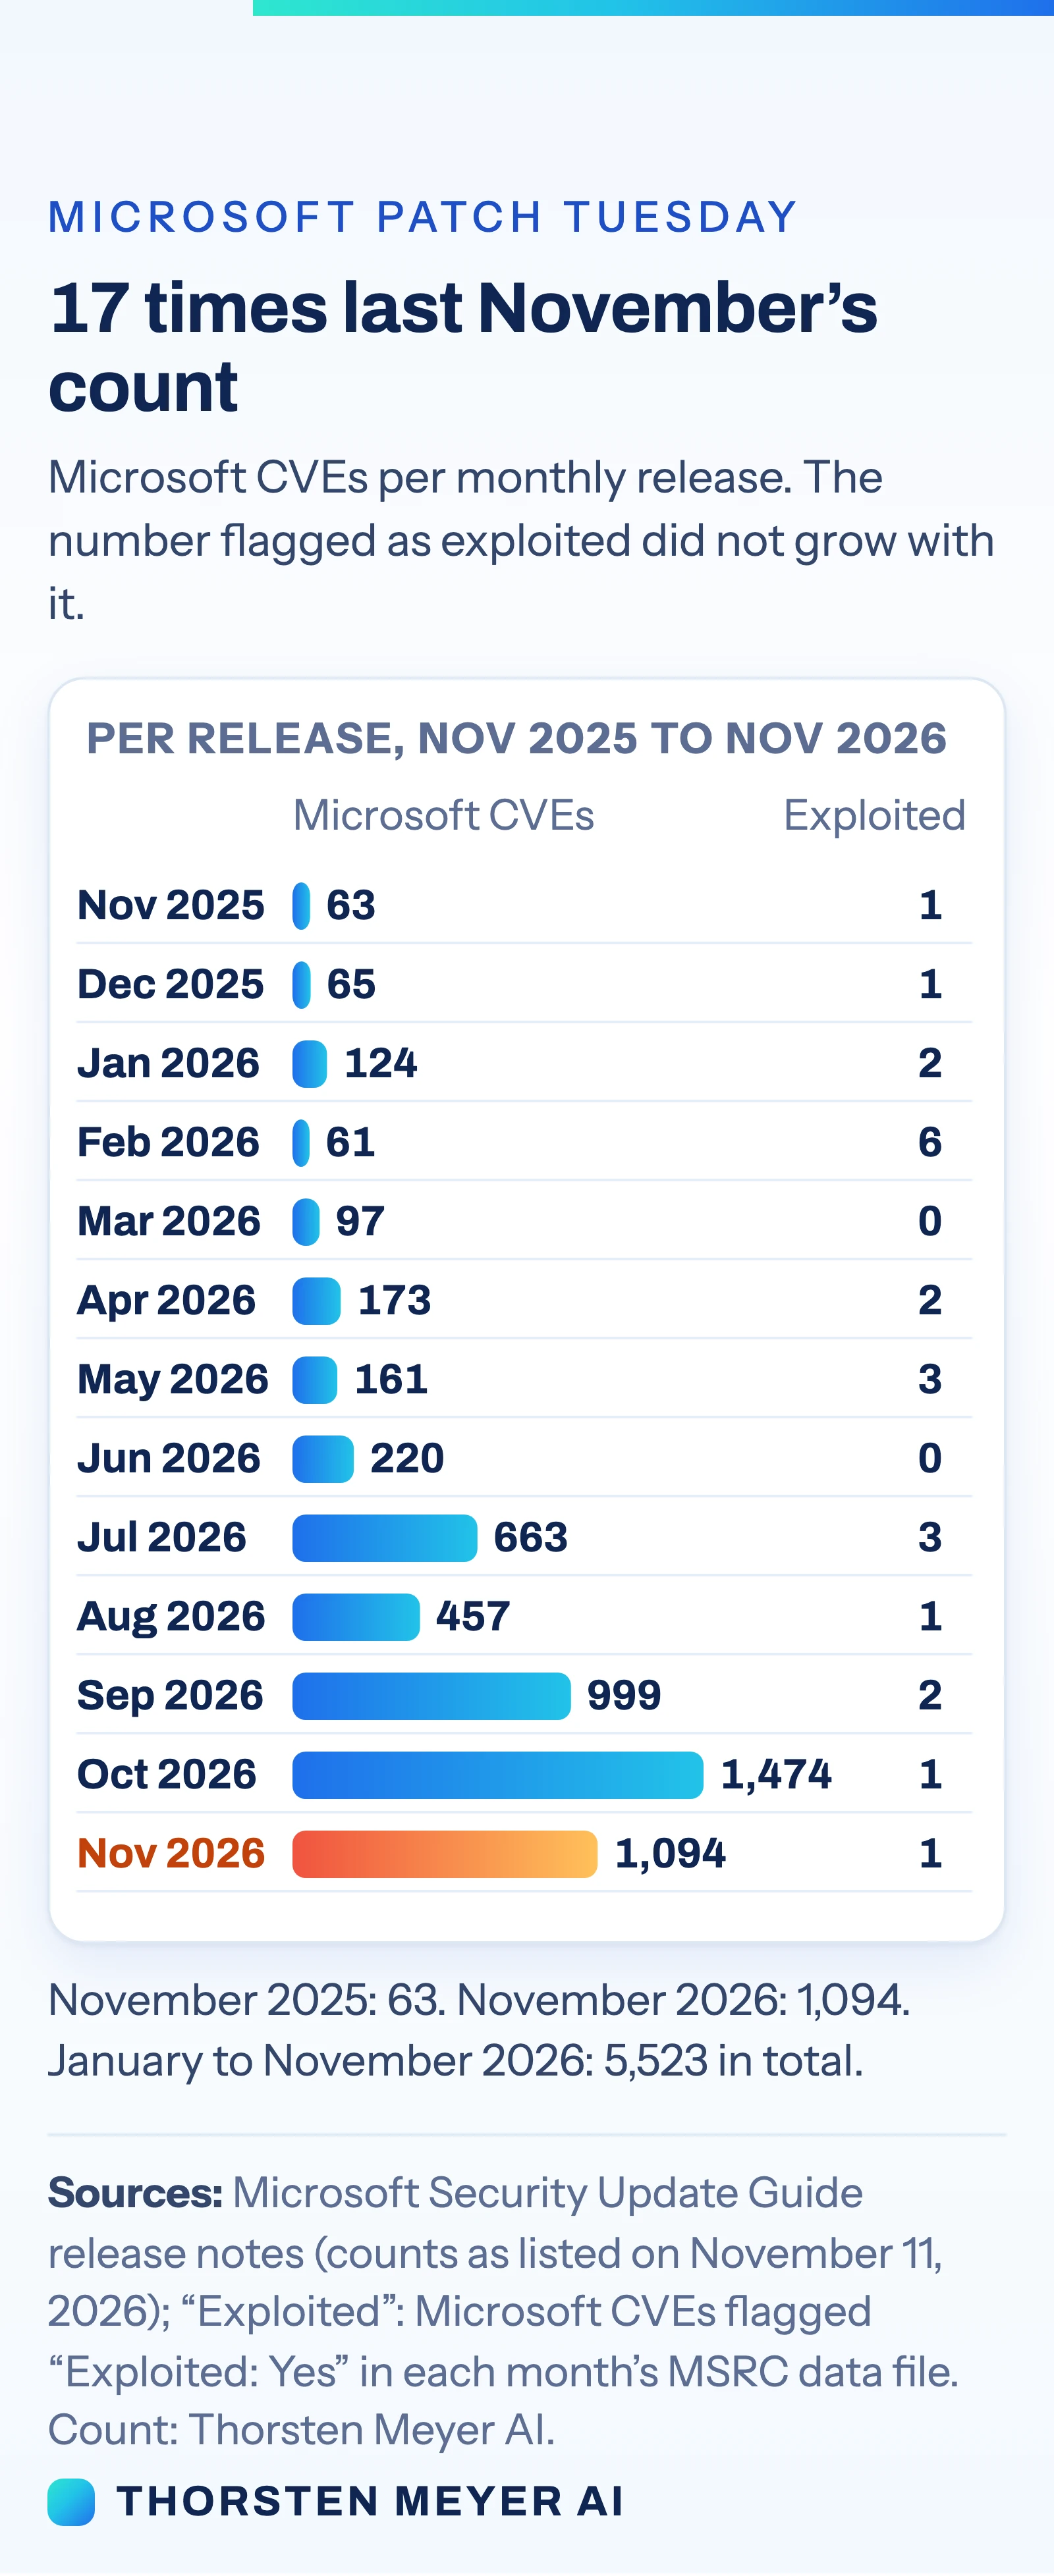
The source’s review of Microsoft release notes reports 63 Microsoft CVEs in November 2025 and 65 in December. Counts rose during 2026, reaching 220 in June, 663 in July, 999 in September and 1,474 in October before November’s 1,094. On that source’s comparison, November’s count is about 17 times the November 2025 figure. The totals describe disclosed CVEs in the cited release notes, not a measure of successful attacks or risk to an individual user.
Microsoft has offered several reasons for larger releases. In April, Tom Gallagher, vice president of engineering at the Microsoft Security Response Center, wrote that AI can help discover more issues across a broader surface. In May, he said advanced AI models are part of the discovery process, while also pointing to improved automation and broader contributions from outside researchers. Microsoft said it expected releases to keep trending larger for some time and said it was not changing its bug bar.
The source analysis found that 24 November CVE credit lines named work done using an AI model: 23 referenced GLM from z.ai and one referenced Claude. Those researcher credits do not reveal what tools Microsoft used internally, or establish how much AI contributed to the total release.
““This is not driven by any one model or any one change.””
— Tom Gallagher, in the same May post
Questions on Scope and Availability
Microsoft has not said how many of November’s vulnerabilities were discovered with AI, and the researcher credit lines do not settle that question. The source also reports differing November counts based on publication date: 1,094 in Microsoft’s release notes and 1,093 in Krebs on Security’s count of fixes published November 10, with one related CVE published November 5.
For the Outlook flaw, the source does not establish the scale or duration of exploitation, or how many users may have been affected. For Paint, reports say the patched version was not visible to some users, but the source does not provide a complete account of availability by region, device or update channel.
Check Patches and Paint Version
Users and IT teams should apply the November Outlook and Office updates relevant to their systems, then review Microsoft’s affected-product guidance for applicable Critical server vulnerabilities. The source recommends checking Paint through the Microsoft Store and confirming that the installed version is 11.2609.401.0 or later. Microsoft has not provided, in the supplied material, a timeline for when the Paint update will reach users who cannot yet see it.
Key Questions
How many CVEs did Microsoft list in its November release?
Microsoft’s November 10, 2026, release notes list 1,094 Microsoft CVEs. Krebs on Security counted 1,093 published that day; the source attributes the difference to a CVE published November 5.
Which vulnerability was already being exploited?
The source identifies CVE-2026-124194 in Outlook as exploited before the fix. It says opening a crafted file can expose a user’s NTLMv2 password hash, and reports that CISA added the flaw to its exploited-vulnerabilities catalog on November 10.
Did AI account for the large number of fixes?
Microsoft has said AI is one part of vulnerability discovery, along with automation and outside research. It has not disclosed how many of the November fixes came from AI; researcher credit lines alone cannot establish that share.
How can users check whether they have the Paint fix?
The source identifies Paint version 11.2609.401.0 as the working version and recommends checking for updates through the Microsoft Store. PC Gamer reported that the update was still unavailable to some users.
Source: Thorsten Meyer AI